

Accurate Hot Selling 303 Exam Dumps 2026 Newly Released
Get 100% Authentic F5 303 Dumps with Correct Answers
NEW QUESTION # 68
Refer to the exhibit.
The LTM devices LTM3 and LTM2 have four Traffic Groups defined with approximately the sar of failover objects defined in each group.
- Traffic Groups A and C have Default Device set to LTM1
- Traffic Groups B and D have Default Device set to LTM2.
- Traffic Groups B and C do NOT have Auto Failback enabled.
- Traffic Groups A and D have Auto Fallback enabled with a timeout
value of 60 seconds.
Both LTM devices are healthy and able to pass traffic for any Traffic Group. LTM1 loses connectivity on interface 1.4. The LTM Specialists notified 60 seconds after the interface goes down.
What is the state of the Traffic Groups on each LTM device?
- A. LTM1: Traffic Groups A, B, C, and D
LTM2: No Traffic Groups - B. LTM1: No Traffic Groups
LTM2: Traffic Groups A, B. C, and D - C. LTM1: Traffic Group C
LTM2: Traffic Groups A, B, and 0 - D. LTM1: Traffic Groups B and C
LTM2: Traffic Groups A and 0
Answer: B
Explanation:
If the 1.4 port is down and failsafe is triggered, the whole machine will become a standby, and all Traffic Groups will be cut away, and no Traffic Group will remain.
NEW QUESTION # 69
Refer to the exhibit.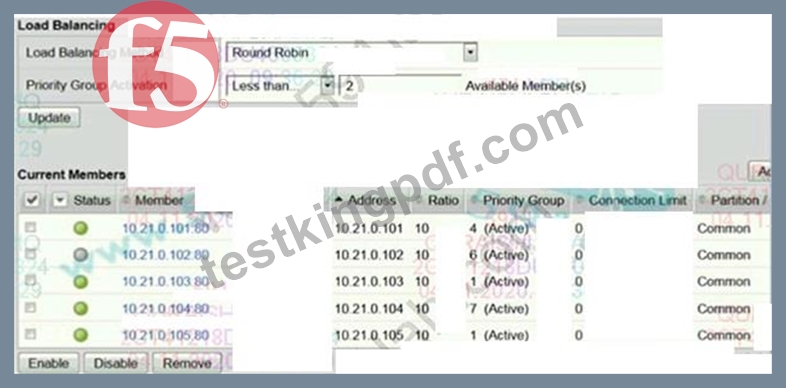
Which two pool members are eligible to receive new connections? (Choose two)
- A. 10.21.0.103.80
- B. 10.21.0.105.80
- C. 10.21.0.101.80
- D. 10.21.0.104.80
- E. 10.21.0.102.80
Answer: C,D
NEW QUESTION # 70
Refer to the exhibit. An LTM Specialist creates a virtual server to load balance traffic to a pool of HTTPS servers. The servers use client certificates for user authentication. The virtual server has clientssl, serverssl, and http profiles enabled. Clients are unable to connect to the application through the virtual server, but they are able to connect to the application servers directly. Which change to the LTM device configuration will resolve the problem?
- A. Use the serverssl-insecure-compatible serverssl profile.
- B. Install the client's issuing Certificate Authority certificate on the LTM device.
- C. Install the server certificate/key and enable Proxy SSL.
- D. Configure the clientssl profile to require a client certificate.
Answer: C
NEW QUESTION # 71
An LTM Specialist needs to modify the logging level for tcpdump execution events. Checking the BigDB Key, the following is currently configured:
sys db log.tcpdump.level {
value "Notice"
}
Which command should the LTM Specialist execute on the LTM device to change the logging level to informational?
- A. tmsh set /sys db log.tcpdump.level status informational
- B. tmsh modify /sys db log.tcpdump.level value informational
- C. tmsh modify /sys db log.tcpdump.level status informational
- D. tmsh set /sys db log.tcpdump.level value informational
Answer: B
NEW QUESTION # 72
An LTM device has a virtual server mapped to www5f.com with a pool assigned. The objects are defined as follows:
Virtual server. Destination 192.168.245.100.443 netmask 255.255.255.0
Persistence: Source address persistence netmask 255.0.0.0
SNAT:AutoMap
Profiles: HnP/TCP
How should the BIG-IP Administrator modify the persistence profile so that each unique IP address creates a persistence record?
- A. netmask 0.0.0.0
- B. netmask 255.255.255.255
- C. netmask 255.256.255.0
- D. netmask 255.255.0.0
Answer: B
NEW QUESTION # 73
The LTM device is configured for RADIUS authentication. Remote logins are failing and the LTM Specialist must verify the RADIUS configuration.
How should the LTM Specialist check the RADIUS server and shared secret configured on the LTM device?
- A. tmsh show running-config /auth radius
- B. tmsh show running-config /sys auth radius
- C. tmsh show running-config /sys auth radius-server
- D. tmsh show running-config /auth configuration
Answer: A
NEW QUESTION # 74
-- Exhibit -
-- Exhibit --
Refer to the exhibit.
A client attempts to connect from a Google Chrome browser to a virtual server on a BIG-IP LTM. The virtual server is SSL Offloaded. When the client connects, the client receives an SSL error. After trying Mozilla Firefox and Internet Explorer browsers, the client still receives the same errors.
The LTM Specialist does an ssldump on the virtual server and receives the results as per the exhibit.
What is the problem?
- A. The BIG-IP LTM is NOT listening on port 443.
- B. The client needs to be upgraded to the appropriate cipher-suite.
- C. The BIG-IP LTM is NOT serving a certificate.
- D. The SSL key length is incorrect.
Answer: C
NEW QUESTION # 75
A BIG-IP Administrator is receiving intermittent reports from users that SSL connections to the BIG-IP device are failing. Upon checking the log files, the BIG-IP Administrator notices the following error message:
ere tmm<instance>[<pid>]: 01260008:3: SSL transaction (TPS) rate limit
reached
After reviewing statistics, the BIG-IP Administrator notices there are a maximum of 1200 client- side SSL TPS and a maximum of 800 server-side SSL TPS.
What is the minimum SSL license limit capacity the BIG-IP Administrator should upgrade to handle this peak?
- A. 0
- B. 1
- C. 2
- D. 3
Answer: D
NEW QUESTION # 76
A BIG-IP Administrator is working with a BIG-IP device and discovers that one of the Interfaces on a Trunk is DOWN.
What is the reason for this Interface status?
- A. There is NO default route configured for this trunk
- B. The switch is NOT connected to the Interface
- C. There is NO transceiver installed on the Interface
- D. The media speed of the interface has NOT been set
Answer: B
NEW QUESTION # 77
A virtual server with SNAT automap enabled selects pool member 10.20.0.10.443 for the server-side flow.
The client side flow source IP is 192.168.0.10 .
Which source IP should be expected inthe server-side connection?
- A. 10.20.0.1
- B. 10.50.0.2
- C. 10.20.0.2
- D. 192.168.0.10
Answer: C
NEW QUESTION # 78
What should the BIG-IP Administrator do to apply and activate a hotfix to a BIG-IP device that is currently running version 11.0.0 on active partition HD1.1?
- A. 1. set partition HD1.2 active
2. apply a hotfix to partition HD1.2 - B. 1. confirm that 11.0.0 is installed on inactive partition HD1.2
2. apply a hotfix to partition HD 1.2
3. activate partition HD1.2 - C. 1. activate partition HD1.2
2 confirm version 11.0.0 on partition HD1.2
3. install a hotfix on partition HD1.2 - D. 1. reactivate the license on partition HD1.1
2. apply a hotfix to partition HD1.1
Answer: B
NEW QUESTION # 79
Which of the following is NOT a valid method for learning about a new application in BIG-IP ASM?
- A. Analyzing an application's logs
- B. Using the Attack Signature Learning feature
- C. Manually defining an application profile
- D. Automatic Policy Building
Answer: A
NEW QUESTION # 80
A webserver is being overloaded with HTTPS traffic. To decrease the load on the server, the LTM Specialist and the Server. Administrator decide to perform SSL offloading on the LTM device. The configuration of the virtual server is as follows:
Which change must be made to the configuration to perform SSL offloading?
- A. Remove the clientssl and http profiles
- B. Remove the clientssl and serverssl profiles
- C. Remove the severssl profile
- D. Remove the clients profile
Answer: C
NEW QUESTION # 81
Refer to the exhibit. A virtual server is set up on an LTM device as follows:
Virtual server address 78.24.213.79
Default Persistence Profile. source_addr, 600s.
Pool Name. Pool1
Pool Members: 10.72.250.52:80 and 10.72.250.60:80 (both on Internal
Vlan)
There are several current connections to the virtual server, and pool member 10.72.250.52:80 has been set to a "Disabled" state.
A tcpdump on the Internal Vlan shows traffic going to 10.72.250.52:80.
How soon after the persistence table query was run can existing connections be refreshed/renewed to ensure that no requests are sent to 10.72.250.52?
- A. 590 seconds
- B. 460 seconds
- C. 539 seconds
- D. 196 seconds
- E. 591 seconds
Answer: C
NEW QUESTION # 82
Refer to the exhibit. A BIG-IP Administrator configures a now VLAN on an HA pair of devices that does NOT yet have any traffic. This action causes the assigned traffic group to fail over to the standby device. Which VLAN setting should be changed to prevent this issue?
- A. Customer Tag
- B. Source Check
- C. Auto Last Hop
- D. Fail-safe
Answer: D
NEW QUESTION # 83
A web developer needs a virtual server configured for an application.
The application details are asfollows:
Application is accessed on port 443.
The application traffic is encrypted by the server.
HTTP is not being used. No data manipulation is necessary.
Throughput is critical.
NO connections are terminated on the LTM.
Which configuration provides thebest performance?
A)
B)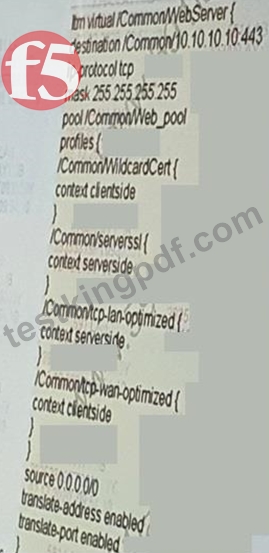
C)
D)
- A. Option
- B. Option
- C. Option
- D. Option
Answer: B
NEW QUESTION # 84
Which of the following is a typical example of an attack signature in BIG-IP ASM?
- A. A redirect URL leading to an external website
- B. A request that attempts to inject SQL commands into a form input
- C. A user request to access a valid webpage
- D. A request for a static image file
Answer: B
NEW QUESTION # 85
-- Exhibit -
-- Exhibit --
Refer to the exhibit.
A failover has just occured on BIG-IP1. BIG-IP2 is now active and manages traffic as expected. Both Bigip's are set with a gateway failsafe to check the reachability of the main border router. Switches have performed as expected.
Where should the LTM Specialist check for potential issues?
- A. Network Interface 2.2 of BIG-IP 1
- B. Network Interface 2.2 of BIG-IP 2
- C. Network Interface 2.1 of BIG-IP 1
- D. Network Interface 2.1 of BIG-IP 2
- E. Network Interface 1.1 of BIG-IP 1
- F. Network Interface 1.1 of BIG-IP 2
Answer: C
NEW QUESTION # 86
A BIG-IP Administrator is performing maintenance on the active BIG-IP device of an HA pair. The BIG-IP Administrator needs to minimize traffic disruptions.
What should the BIG-IP Administrator do to start the maintenance activity?
- A. Disable switch ports of the BIG-IP device.
- B. Move resources to a new Traffic Group.
- C. Force the BIG-IP device to standby.
- D. Reboot the BIG-IP device.
Answer: C
NEW QUESTION # 87
Refer to the exhibit. A BIG-IP Administrator needs to configure health monitors for a newly configured server pool named Pool_B. Which health monitor settings will ensure that all pool members will be accurately marked as available or unavailable?
- A. HTTPS, HTTP, FTP, and ICMP, with the Availability Requirement of all health monitors
- B. HTTPS and HTTP with the Availability Requirement of at least one health monitor
- C. HTTPS, HTTP, FTP, and SSH, with the Availability Requirement of at least one monitor
- D. HTTPS, HTTP, FTP, and SSH with the Availability Requirement of all health monitors
Answer: C
Explanation:
From the port, the four members are HTTP, FTP, HTTPS, and SSH applications. If you want to monitor at the same time, you must configure at least one.
NEW QUESTION # 88
A BIG-IP Administrator needs to apply a license to the BIG-IP system to increase the user count from the base license. Which steps should the BIG-IP Administrator?
- A. System > License > Re-activate > Base Registration> Edit
- B. Device Management > Devices > Select BIG-IP System > Update
- C. System License > Re-activate> Add-On Registration> Edit
- D. System > Configuration >Device > General
Answer: C
NEW QUESTION # 89
Users report that traffic is negatively affected every time a BIG-IP device fails over. The traffic becomes stabilized after a few minutes.
What should the BIG-IP Administrator do to reduce the impact of future failovers?
- A. Enable Failover Multicast Configuration
- B. Configure MAC Masquerade
- C. Configure a global SNAT Listener
- D. Set up Failover Method to HA Order
Answer: B
NEW QUESTION # 90
......
To prepare for the F5 303 certification exam, individuals can take the F5 BIG-IP ASM Specialist course, which covers all the topics included in the exam. 303 course is available online and in-person, and it provides hands-on experience with the F5 BIG-IP ASM tool. Additionally, F5 offers a variety of study materials, including practice exams, study guides, and online courses, to help individuals prepare for the exam.
Dumps of 303 Cover all the requirements of the Real Exam: https://www.testkingpdf.com/303-testking-pdf-torrent.html
New Training Course 303 Tutorial Preparation Guide: https://drive.google.com/open?id=1zVYhlqe7gJUszUxvGvelpTYF_THxoM-a
